Website Chatbot Security: The Loftx Approach
Narasimhan Vallur | 2026-11-10
Last updated: November 13, 2026
Property management website chatbot security is a buying question as much as a technical one. Before your team adds chat, it needs to understand where conversations go, who can access them and how business information is used.
LOFTx.ai addresses those questions through documented Azure hosting, encryption, organization-level access controls and an enterprise AI approach that does not use your data to train foundation models. You can evaluate the customer experience and the data-handling commitments together.
Website chatbot security starts with the right information
A website visitor may provide a name, contact details and questions about a home or service. Loftx uses the conversation and relevant business information to support the interaction. Its security documentation describes data minimization: an AI task receives the information it needs, rather than the organization's entire dataset.
For a PMC, keep public leasing and policy answers distinct from private account details. For a vendor, keep product explanations distinct from customer records that require authenticated access. Define the purpose of each website action during setup.
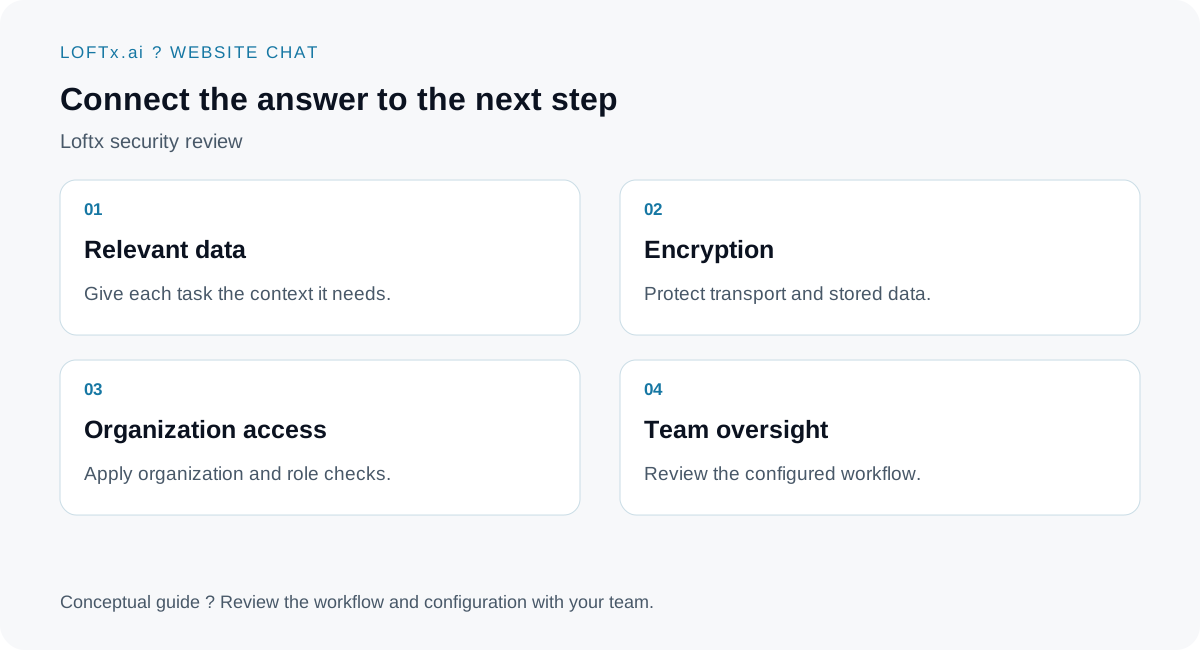
A summary of published Loftx controls, not a certification badge.
Your data stays yours
Loftx's security page states that its AI runs on Azure OpenAI Service and that prompts and responses are not used to train the foundation models. It also describes separation of customer portfolios, financial information and conversation history.
This is a specific data-use commitment. It does not mean conversations are never stored or that every record is automatically deleted after a fixed number of days. Retention and deletion are separate questions to discuss for your service.
For teams evaluating a new AI tool, that distinction makes the review clearer: ask both how information is used by the AI provider and how the application retains the records needed to deliver the service.
Controls your team can review
| Question | Loftx's published approach |
|---|---|
| Where does the core platform run? | Database, application servers and AI in US Azure regions |
| Is data encrypted? | TLS in transit and Azure encryption for stored data |
| How is customer access separated? | Organization checks and role- and page-based access |
| Are service credentials in the widget? | PMS, CRM and AI service keys remain on the server |
| Who else processes communications? | Specialist providers for services such as messaging; current list available on request |
| How long is information kept? | For the needs of the service; deletion requests handled according to instructions and applicable requirements |
These statements summarize Loftx's published commitments. Ask for the current details relevant to your deployment, including any communication providers you enable.
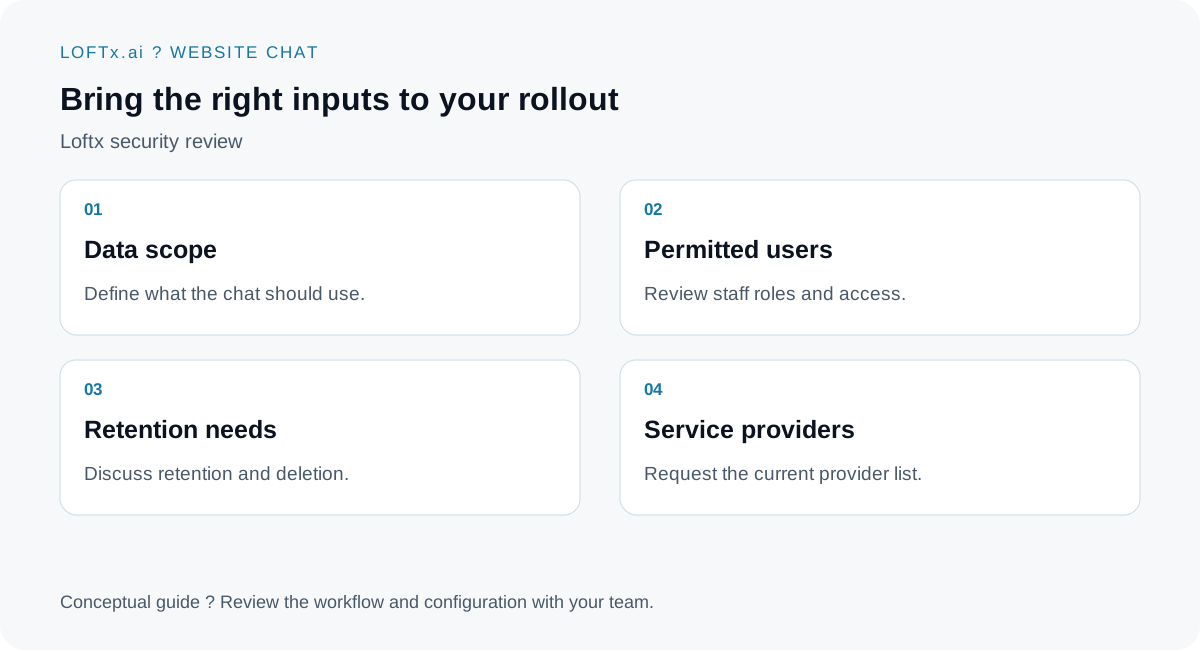
Bring your requirements to the review so the answers map to your actual use.
Be precise about SOC 2
Loftx describes controls built around the AICPA SOC 2 Trust Services Criteria. Its security page explicitly states that this is not an audited SOC 2 report. If your procurement process requires an audited report, raise that requirement directly rather than interpreting alignment with the criteria as certification.
That clarity lets your team make a decision using the actual evidence. It also avoids mixing the certifications of an infrastructure provider with the assurance status of an application running on it.
Pair access controls with a useful customer experience
Security questions do not remove the need for effective engagement. Loftx's website chat provides company-specific answers, configurable next steps and live takeover. Your team can review the experience while checking that actions and access match their intended purpose.
Use test inquiries for a public policy question, a request for private account information and a request for a person. Review what the visitor sees and what the authorized team sees. A successful rollout should be clear on both sides.
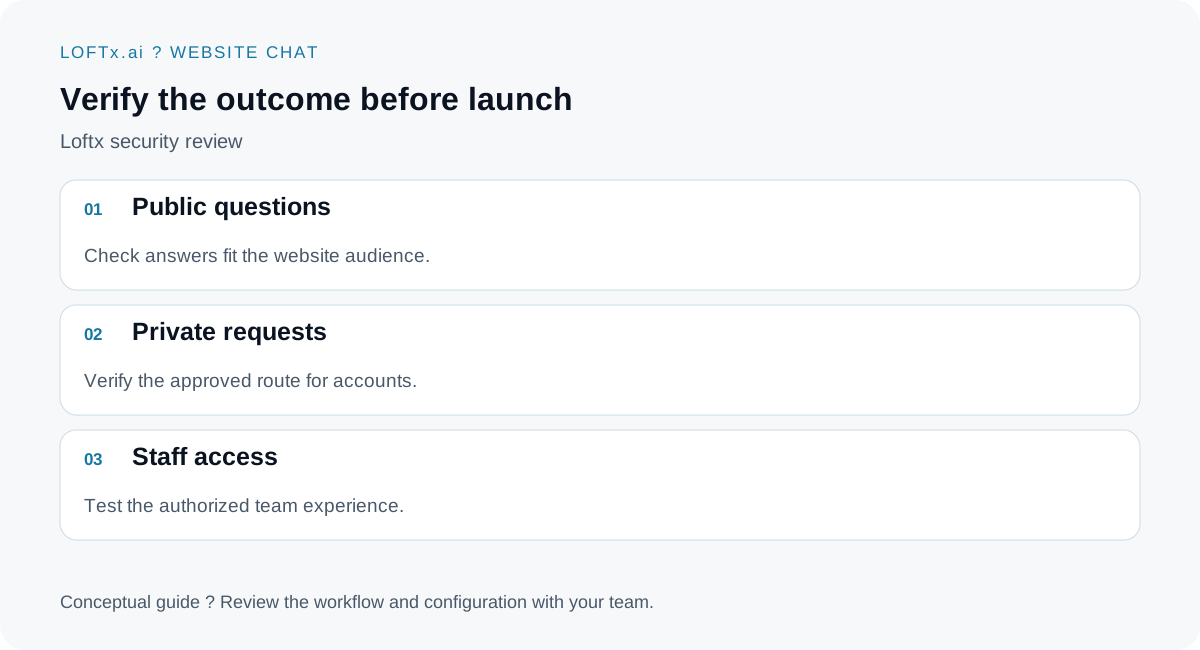
Suggested rollout checks; validate them for your configured environment.
Bring security into your Loftx demo
Review the website chat experience alongside the security documentation so procurement covers the actual visitor and staff workflow.
Book a demo with your security questionnaire and preferred website workflow. Review the published security details, the visitor experience and the staff handoff together. Get the information you need to choose website chat with confidence.